Continuous Third-Party Monitoring: What NIST Actually Requires
NIST publishes the guidance that shapes how organizations set security requirements for their supply chains: NIST SP 800-53, Security and Privacy Controls for Information Systems and Organizations; the NIST Cybersecurity Framework; and NIST SP 800-161r1, Cybersecurity Supply Chain Risk Management Practices for Systems and Organizations. All three point in the same direction. A vendor's security posture is not a fact you establish once at onboarding. It is a condition you track for as long as the relationship lasts. The guidance described here reflects Cybersecurity Framework 2.0, SP 800-53 Rev. 5 and SP 800-161r1, the current editions of each.
Continuous third-party monitoring is the ongoing, externally observable measurement of a vendor's cyber risk posture between formal assessments. Instead of relying on a questionnaire answered once a year, a monitoring program collects evidence from public and technical sources on a recurring basis, detects changes in a vendor's exposure as they happen, and records what was found, when it was found, and what was done about it. The output is not a single verdict at a single moment. It is a continuous record of risk across every vendor in the portfolio.
That distinction matters most to the people who have to defend the program. A governance, risk and compliance team is not judged on whether it collected assessments. It is judged on whether it can prove that every vendor was assessed, that every finding was routed to an owner, and that nothing slipped through untracked.
Continuous Monitoring Replaces the Annual Snapshot With a Live Record
Point-in-time assessment has a structural problem. The questionnaire captures a vendor's self-reported posture on the day it was completed. The certificate captures an auditor's opinion at the time of audit. Neither one updates when the vendor exposes a new management interface, lets a certificate lapse, inherits a critical vulnerability from a software provider, or gets absorbed into a parent company with weaker controls.
Continuous monitoring fills that gap with observed evidence rather than attestation. It watches the technical and public footprint of each vendor, flags material change, and gives the risk team a reason to act before an incident surfaces the exposure. That is the practical argument for the approach, and it is worth reading alongside the operational case for the model: how continuous monitoring reduces cyber risk across a vendor portfolio.
Two things separate a monitoring program from a monitoring tool. The first is coverage: every vendor in scope, not just the top tier. The second is accountability: a documented decision attached to every finding. Coverage without accountability produces alerts nobody owns. Accountability without coverage produces a tidy record of the vendors you happened to look at.
NIST SP 800-53 Puts Supply Chain Risk Inside the Control Set
NIST SP 800-53 sets out the security and privacy controls that protect sensitive government information and citizens' personal information from cyber attack. It helps federal agencies and their contractors meet the requirements of the Federal Information Security Modernization Act. The controls span operational, technical and management safeguards, and they evolve as the threat landscape, infrastructure models and business models shift. The objective does not change: maintain the integrity, confidentiality and security of federal information systems.
Revision 5 brought several changes that matter to third-party programs:
- Privacy controls integrated directly into the control set
- Controls scoped for different interest groups, including systems engineers, software developers, enterprise architects, and mission and business owners
- Closer integration with other risk management and cybersecurity approaches, including the NIST Cybersecurity Framework
- New controls added on the basis of threat intelligence
- Supply chain risk lifted out of the acquisition control family and given a dedicated family of its own
That last change is the one third-party programs felt. Supply chain expectations that used to be a subsection of acquisition policy now carry their own family of controls, which raises supply chain risk from a procurement step to an ongoing organizational responsibility.
How NIST SP 800-53 Treats Third Parties

NIST treats supply chain risk management as a core organizational function rather than a procurement formality. Organizational assets have to be protected across the full system development life cycle, which means supply chain risk to information systems and system components needs a standardized, repeatable process behind it. Educating the acquisition workforce on threats, risk and required security controls is part of that process, not an add-on to it.
The expectations are cumulative rather than sequential. An organization is expected to plan for supply chain risk, build defined processes that address it, assess suppliers and the products and services they deliver, and keep that assessment alive after the contract is signed. The anchor for third-party programs is supplier assessment and review, expressed in Rev. 5 as SR-6: organizations assess and review the supply chain risk associated with a supplier, and with the systems, components and services that supplier provides, at a defined frequency rather than once.
What NIST Expects a Supply Chain Program to Do
- Employ tailored acquisition strategies when purchasing an information system or system component
- Conduct a supplier review before entering a contractual agreement
- Employ safeguards that limit harm from potential adversaries
- Assess the system, component or service before selection, acceptance or update
- Use all-source intelligence analysis, including open-source intelligence, on suppliers and prospective suppliers
- Establish agreements that require notification when a supply chain compromise or relevant change occurs
- Apply analysis or testing, whether organizational or independent, to verify what a supplier claims
Read that list as a program design, and the case for continuous monitoring makes itself. Supplier review before contract, reassessment before update, notification on compromise, and all-source intelligence analysis are not annual events. They are triggered by change, and you cannot respond to change you are not watching.
The Cybersecurity Framework Gives Risk Teams and Vendors a Shared Language
The Cybersecurity Framework works as a common language for risk and cybersecurity communication, both internally from the server room to the board room and externally across stakeholders. It applies across industries and domains. Version 2.0 organizes cybersecurity activity into six functions: Govern, Identify, Protect, Detect, Respond and Recover.
Govern is the addition that changed the third-party conversation. Supply chain risk management now sits inside it, as the Cybersecurity Supply Chain Risk Management category, which puts supplier oversight alongside strategy, roles, policy and oversight rather than treating it as an inventory exercise. The category addresses risk in both directions: the cybersecurity effect an organization has on external parties, and the effect external parties have on the organization.
One outcome in that category names the continuous-monitoring requirement outright. GV.SC-07 expects that risks posed by a supplier, the products and services that supplier provides, and other third parties are understood, recorded, prioritized, assessed, responded to and monitored over the course of the relationship. Every verb in that sentence describes an activity with a date attached, and the phrase "over the course of the relationship" rules out a single assessment at intake.
The rest of the category surrounds that outcome with the governance a GRC team recognizes:
- Determining cybersecurity requirements for suppliers
- Enacting those requirements through a formal agreement such as a contract
- Communicating to suppliers how the requirements will be verified and validated
- Verifying that requirements are met through a range of assessment methodologies
- Planning for the end of the relationship, including offboarding and the retirement of access
- Governing and managing all of the above
The last item is the one GRC teams carry. Governing and managing the process means producing evidence that the process ran, for every supplier, every time.
NIST SP 800-161r1 Is Where Supply Chain Practice Actually Lives
SP 800-53 supplies the controls and the Cybersecurity Framework supplies the shared language, but SP 800-161r1 is the publication that tells an organization how to run cyber supply chain risk management as a program. It covers C-SCRM governance and strategy, roles and responsibilities, the integration of supply chain risk into enterprise risk management, and the tailoring of controls to the criticality of the supplier and the system. It sits alongside the other two rather than replacing either: 800-161r1 points back to the SP 800-53 control set for the controls themselves, and it aligns with the framework's functions for reporting.
For a third-party program, the practical value of 800-161r1 is that it treats supplier oversight as a continuing operation with defined owners, defined triggers and defined records. That is the same program shape continuous monitoring produces, described in NIST's own terms.
Zero Exceptions Tracking Turns Monitoring Into Audit Evidence
Most third-party programs can show an auditor a stack of completed assessments. Far fewer can show the inverse: proof that no vendor was skipped, no finding was quietly dropped, and no risk acceptance was granted without a named owner and a date. That gap is where audit findings come from, and closing it is what zero exceptions tracking does.
Zero exceptions tracking means the program treats an untracked vendor and an untracked finding as the same failure. Every entity in the third-party inventory carries a monitoring state at all times. Every finding carries a disposition. Nothing exists in an undefined middle.
What Zero Exceptions Tracking Requires
- A reconciled inventory. The vendor list in the risk platform matches the vendor list in procurement and accounts payable. Vendors added outside the intake process get surfaced rather than living in a spreadsheet nobody audits.
- A monitoring state on every vendor. Actively monitored, pending onboarding, out of scope with a documented rationale, or offboarded with a date. Four states, no blanks.
- A disposition on every finding. Remediated, mitigated with a compensating control, risk accepted by a named approver, or false positive with the basis recorded. A finding cannot sit unassigned.
- An expiration on every exception. Risk acceptances carry a review date. When the date passes, the exception reopens rather than aging into permanence.
- Escalation that fires on inaction. The absence of a decision triggers the same workflow as a negative decision, so silence is never a path to closure.
The Audit Trail an Assessor Actually Asks For
An assessor testing a third-party program works backward from evidence. The questions are consistent, and a monitoring program built for audit answers all of them from the record rather than from memory:
- Show the full population of third parties in scope, and reconcile it to the source of truth for the period under review.
- For a sample of vendors, show the date monitoring began and prove it has been continuous since.
- For a sample of findings, show when the finding was raised, who it was assigned to, what action was taken, when it closed, and who approved the closure.
- For every risk acceptance, show the approver, the business justification, the compensating control, and the review date.
- Show the vendors that were assessed late or not at all, and the remediation of the process failure that allowed it.
The last question is the one that separates a defensible program from an optimistic one. An auditor who finds a documented, dated, remediated gap generally records a functioning control. An auditor who finds a gap the program did not know about records something worse.
Mapping the Trail Back to NIST
The audit trail is not paperwork added on top of the NIST guidance. It is the guidance made testable. SP 800-53 calls for a planned, standardized process to address supply chain risk to systems and components, and a standardized process is only demonstrable through records that show it ran the same way every time. The expectation to assess a system, component or service before selection, acceptance or update depends on timestamps: you cannot prove an assessment preceded a contract signature without a dated record of both.
The Cybersecurity Framework asks organizations to communicate to suppliers how cybersecurity requirements will be verified and validated, then to verify that they are met, then to keep supplier risk understood, recorded, prioritized, assessed, responded to and monitored for as long as the relationship runs. Verification generates evidence by definition, and monitoring across a relationship generates a dated series of it. The governing and managing outcome is where zero exceptions tracking lives, because governance without a completeness check is a policy document rather than a control.
Continuous monitoring supplies the timestamps. Zero exceptions tracking supplies the completeness. Together they let a GRC team answer an assessor's question in the room instead of opening a two-week evidence hunt.
How Black Kite Supports a Continuous, Auditable Program
Black Kite® measures third-party cyber risk from the outside in, using open standards-based cyber ratings and correlating technical findings to the frameworks GRC teams already report against.
Standards-Based Cyber Ratings, Refreshed Continuously
Black Kite cyber ratings apply across the supply chain risk management expectations in NIST SP 800-53 Rev. 5 and the Cybersecurity Supply Chain Risk Management category of Cybersecurity Framework 2.0. Ratings update as a vendor's observable posture changes, which gives the risk team a dated record of every shift rather than a yearly line item.
Compliance Correlation That Maps Findings to Control Language
Knowing a vendor's cybersecurity maturity means assessing where it stands against the standards you are held to. Black Kite's standards-based approach estimates and assesses third-party compliance levels by correlating cyber risk findings to industry standards and best practices, including NIST SP 800-53, ISO 27001, PCI DSS, HIPAA, GDPR and Shared Assessments. The classification lets a GRC team report vendor posture in the same control language as the rest of the program, which shortens the distance between a technical finding and an audit response.
Probable Financial Impact Based on Open FAIR™
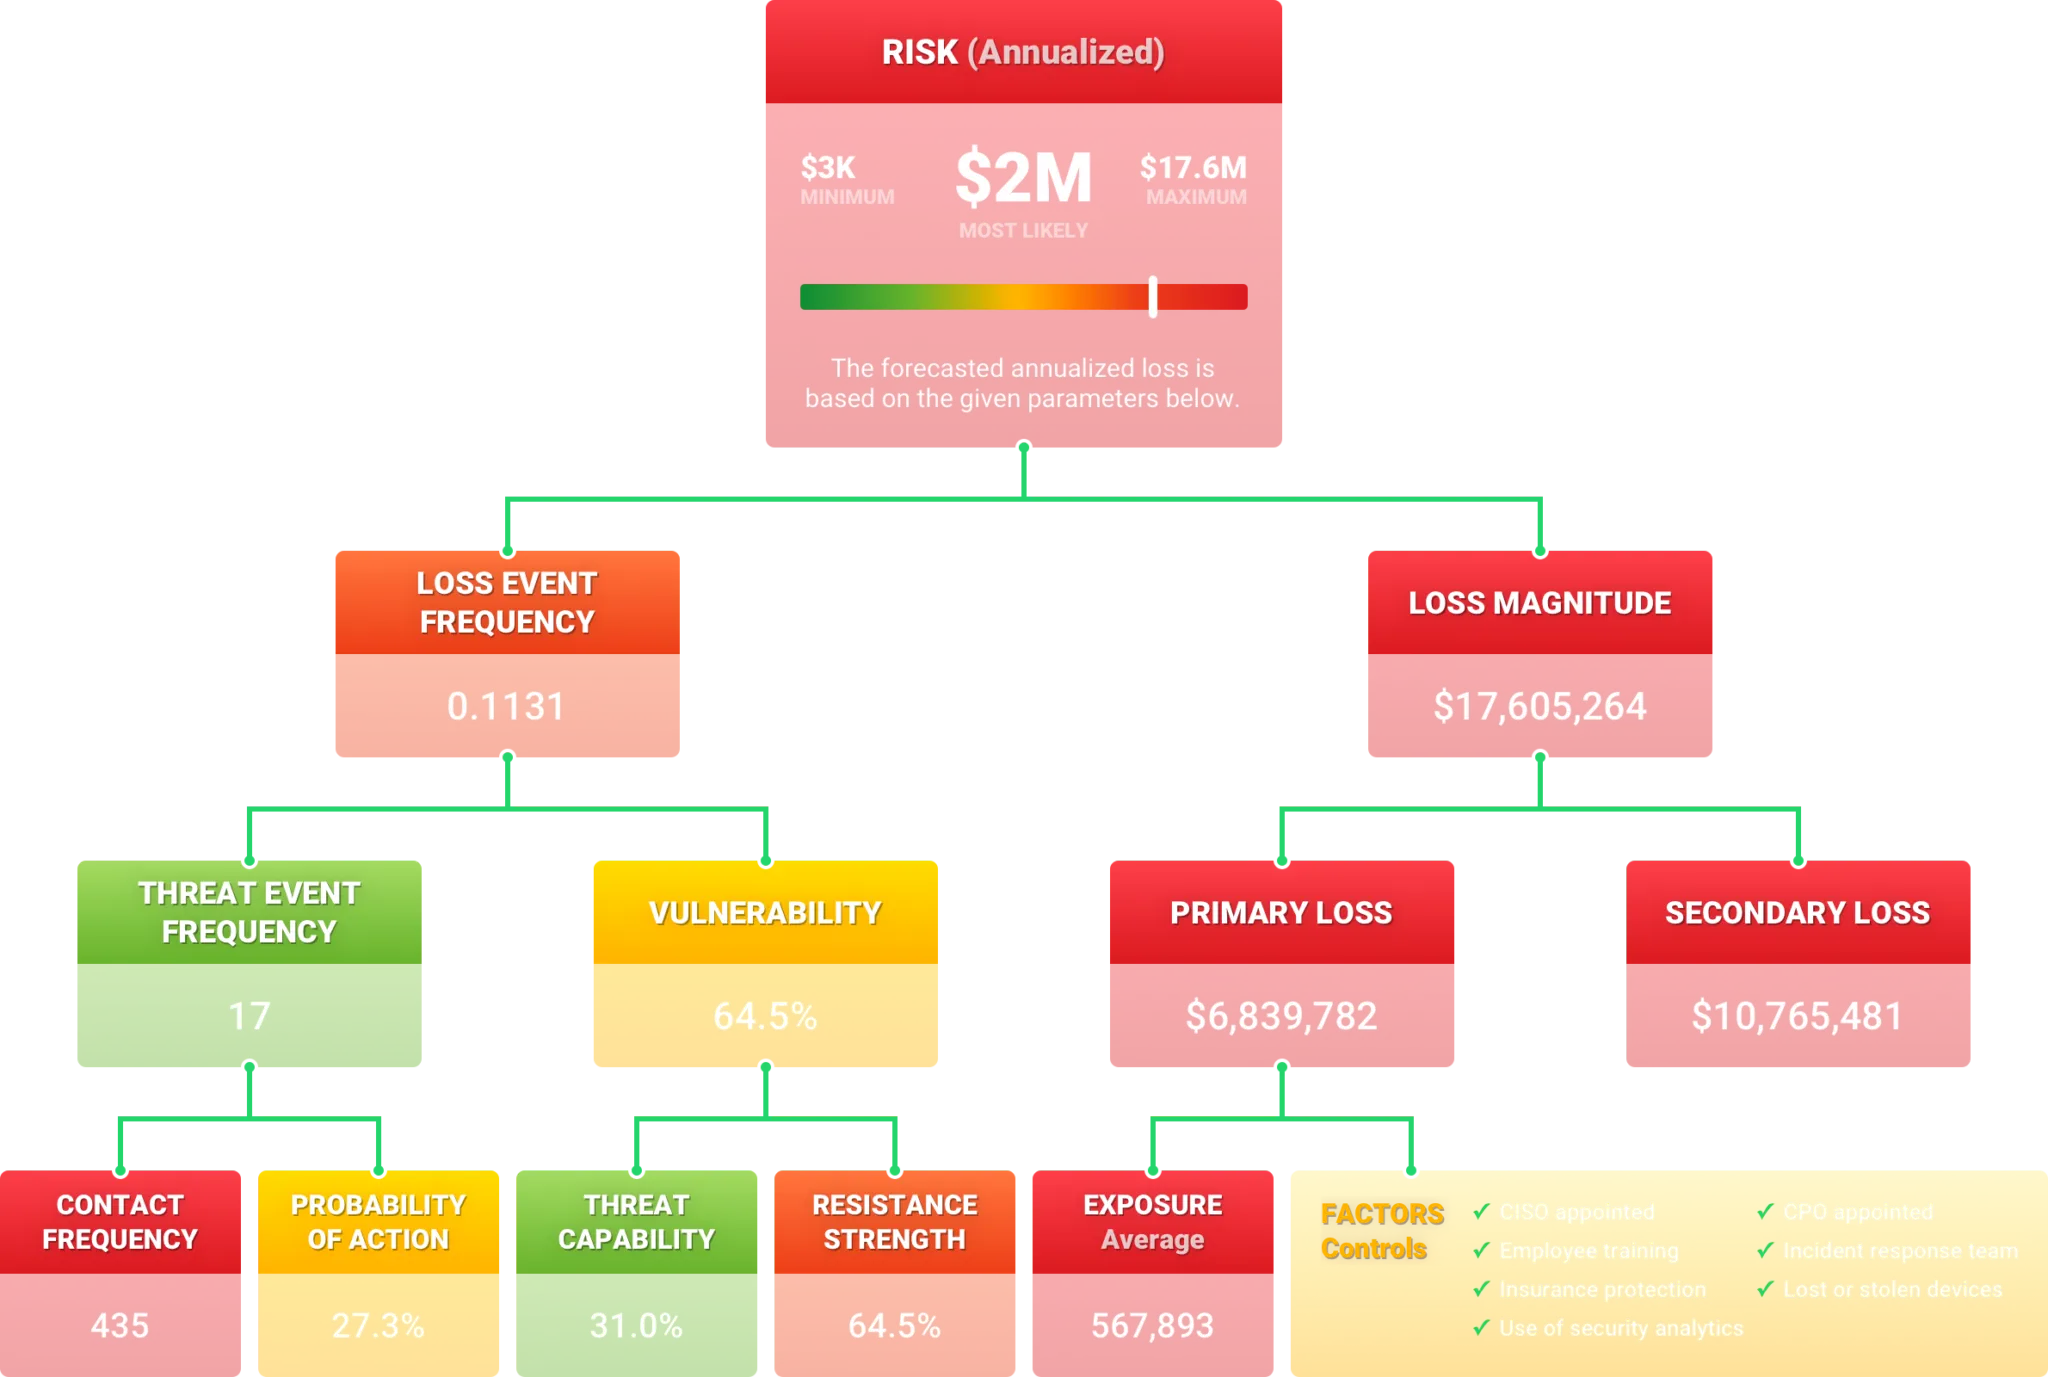
Black Kite uses the Open FAIR model to calculate the probable financial impact if a vendor, partner or supplier experiences a breach, expressed in quantitative business terms. Open FAIR is an international standard Value at Risk model for cybersecurity and operational risk, which keeps the impact estimate inside the kind of standardized, repeatable method NIST expects a supply chain program to use. For a GRC team, financial framing turns a prioritization argument into a budget conversation the business can act on.
Where the Program Maps to NIST
Control identifiers change between revisions. The outcomes above do not. This table is the single place to check which current NIST reference each part of a continuous, auditable program answers to.
Framework | Reference | What it requires | Where Black Kite fits |
|---|---|---|---|
NIST CSF 2.0 | GV.SC-07 | Risks from suppliers, their products and services, and other third parties are understood, recorded, prioritized, assessed, responded to and monitored across the relationship | Continuous outside-in measurement of every vendor in scope, with each change dated and retained as a record |
NIST SP 800-53 Rev. 5 | SR-6, Supplier Assessments and Reviews | Assess and review the supply chain risk of a supplier and the systems, components and services it provides, at a defined frequency | Recurring cyber ratings and compliance correlation that stand as the review record between formal assessments |
NIST SP 800-53 Rev. 5 | SR-2, Supply Chain Risk Management Plan | A documented plan for managing supply chain risk, reviewed and updated on a defined cycle | Portfolio-wide monitoring states and coverage reporting that show the plan is operating, not just written |
NIST SP 800-53 Rev. 5 | SR-3, Supply Chain Controls and Processes | Defined processes to identify and address supply chain risk, with the processes documented for review | Dispositions, approvers and expirations captured on every finding, producing the process evidence an assessor tests |
NIST SP 800-53 Rev. 5 | SR-8, Notification Agreements | Agreements with suppliers requiring notification of supply chain compromise or relevant change | Change detection that tells the risk team when a vendor's exposure shifts, so notification terms can be exercised rather than assumed |
NIST SP 800-161r1 | Cybersecurity Supply Chain Risk Management Practices for Systems and Organizations | Run C-SCRM as a governed program with defined owners, criticality-based tailoring and integration into enterprise risk management | TPCRM data and financial impact estimates that feed supplier oversight into the enterprise risk reporting line |
Questions GRC Teams Ask About Continuous Third-Party Monitoring
What is continuous third-party monitoring?
Continuous third-party monitoring is the ongoing measurement of a vendor's cyber risk posture between formal assessments, using externally observable technical and public evidence rather than self-reported attestation. It detects material change as it happens and records what was found and what was done about it, so the program holds a current view of every vendor instead of a stale view of a few.
Does NIST require continuous monitoring of third parties?
NIST SP 800-53 is mandatory for federal agencies and flows to their contractors through FISMA, while the Cybersecurity Framework is voluntary guidance adopted widely across the private sector. Both call for supplier review before contract, assessment before selection or update, and ongoing verification that cybersecurity requirements are met across the life of the relationship. SP 800-161r1 describes how to operate that as a program. Meeting those expectations on a change-driven basis rather than an annual one is what a continuous program delivers.
How is continuous monitoring different from an annual vendor questionnaire?
A questionnaire captures what a vendor reported on one day. Continuous monitoring observes what is true across the relationship and timestamps every change. The two work together: the questionnaire covers internal controls no outside observer can see, and monitoring keeps the picture current between cycles. Continuous monitoring reduces cyber risk precisely because it shortens the time between a vendor's exposure appearing and your team knowing about it.
What evidence should a third-party monitoring program produce for an audit?
A defensible program produces a reconciled population of third parties, a monitoring state for every vendor with no blanks, a dated disposition for every finding, a named approver and review date for every risk acceptance, and a record of process failures with their remediation. Assemble that as you go and audit preparation becomes a query rather than a project.
How often should third-party risk be reassessed?
Tie reassessment to change rather than to the calendar. Criticality sets the floor for formal reassessment cycles, and continuous monitoring supplies the triggers in between, so a vendor whose exposure shifts is reviewed when it shifts. Continuous monitoring makes that possible across the full portfolio, not only the vendors at the top of the tier list.
Which NIST references should a third-party program cite today?
Cite Cybersecurity Framework 2.0 for the outcomes, SP 800-53 Rev. 5 for the controls, and SP 800-161r1 for the practice. Programs still citing withdrawn acquisition-family controls or the 2018 framework version are pointing at guidance NIST has since replaced, which is a finding waiting to happen in an audit that checks sources.
Build a Third-Party Program That Can Prove Itself
NIST guidance sets the expectation: a standardized, documented, repeatable process for supply chain risk, verified rather than assumed, and sustained for as long as the supplier relationship lasts. Continuous monitoring meets the standardized and verified part. Zero exceptions tracking meets the documented and repeatable part. A program with both can name every vendor in scope, show when each finding opened and closed, and hand an assessor the record on request.
See how Black Kite builds that record across your vendor portfolio.