Manufacturing Cyber Risk Runs Through the Supply Chain
Black Kite gives manufacturers continuous visibility into the suppliers behind their production lines to keep goods moving.

Trusted by
Manufacturers rely on Black Kite to see the supplier risk their internal tools miss.
Manufacturing's Digital Leap Created a Cyber Chasm. It's Time to Bridge It.
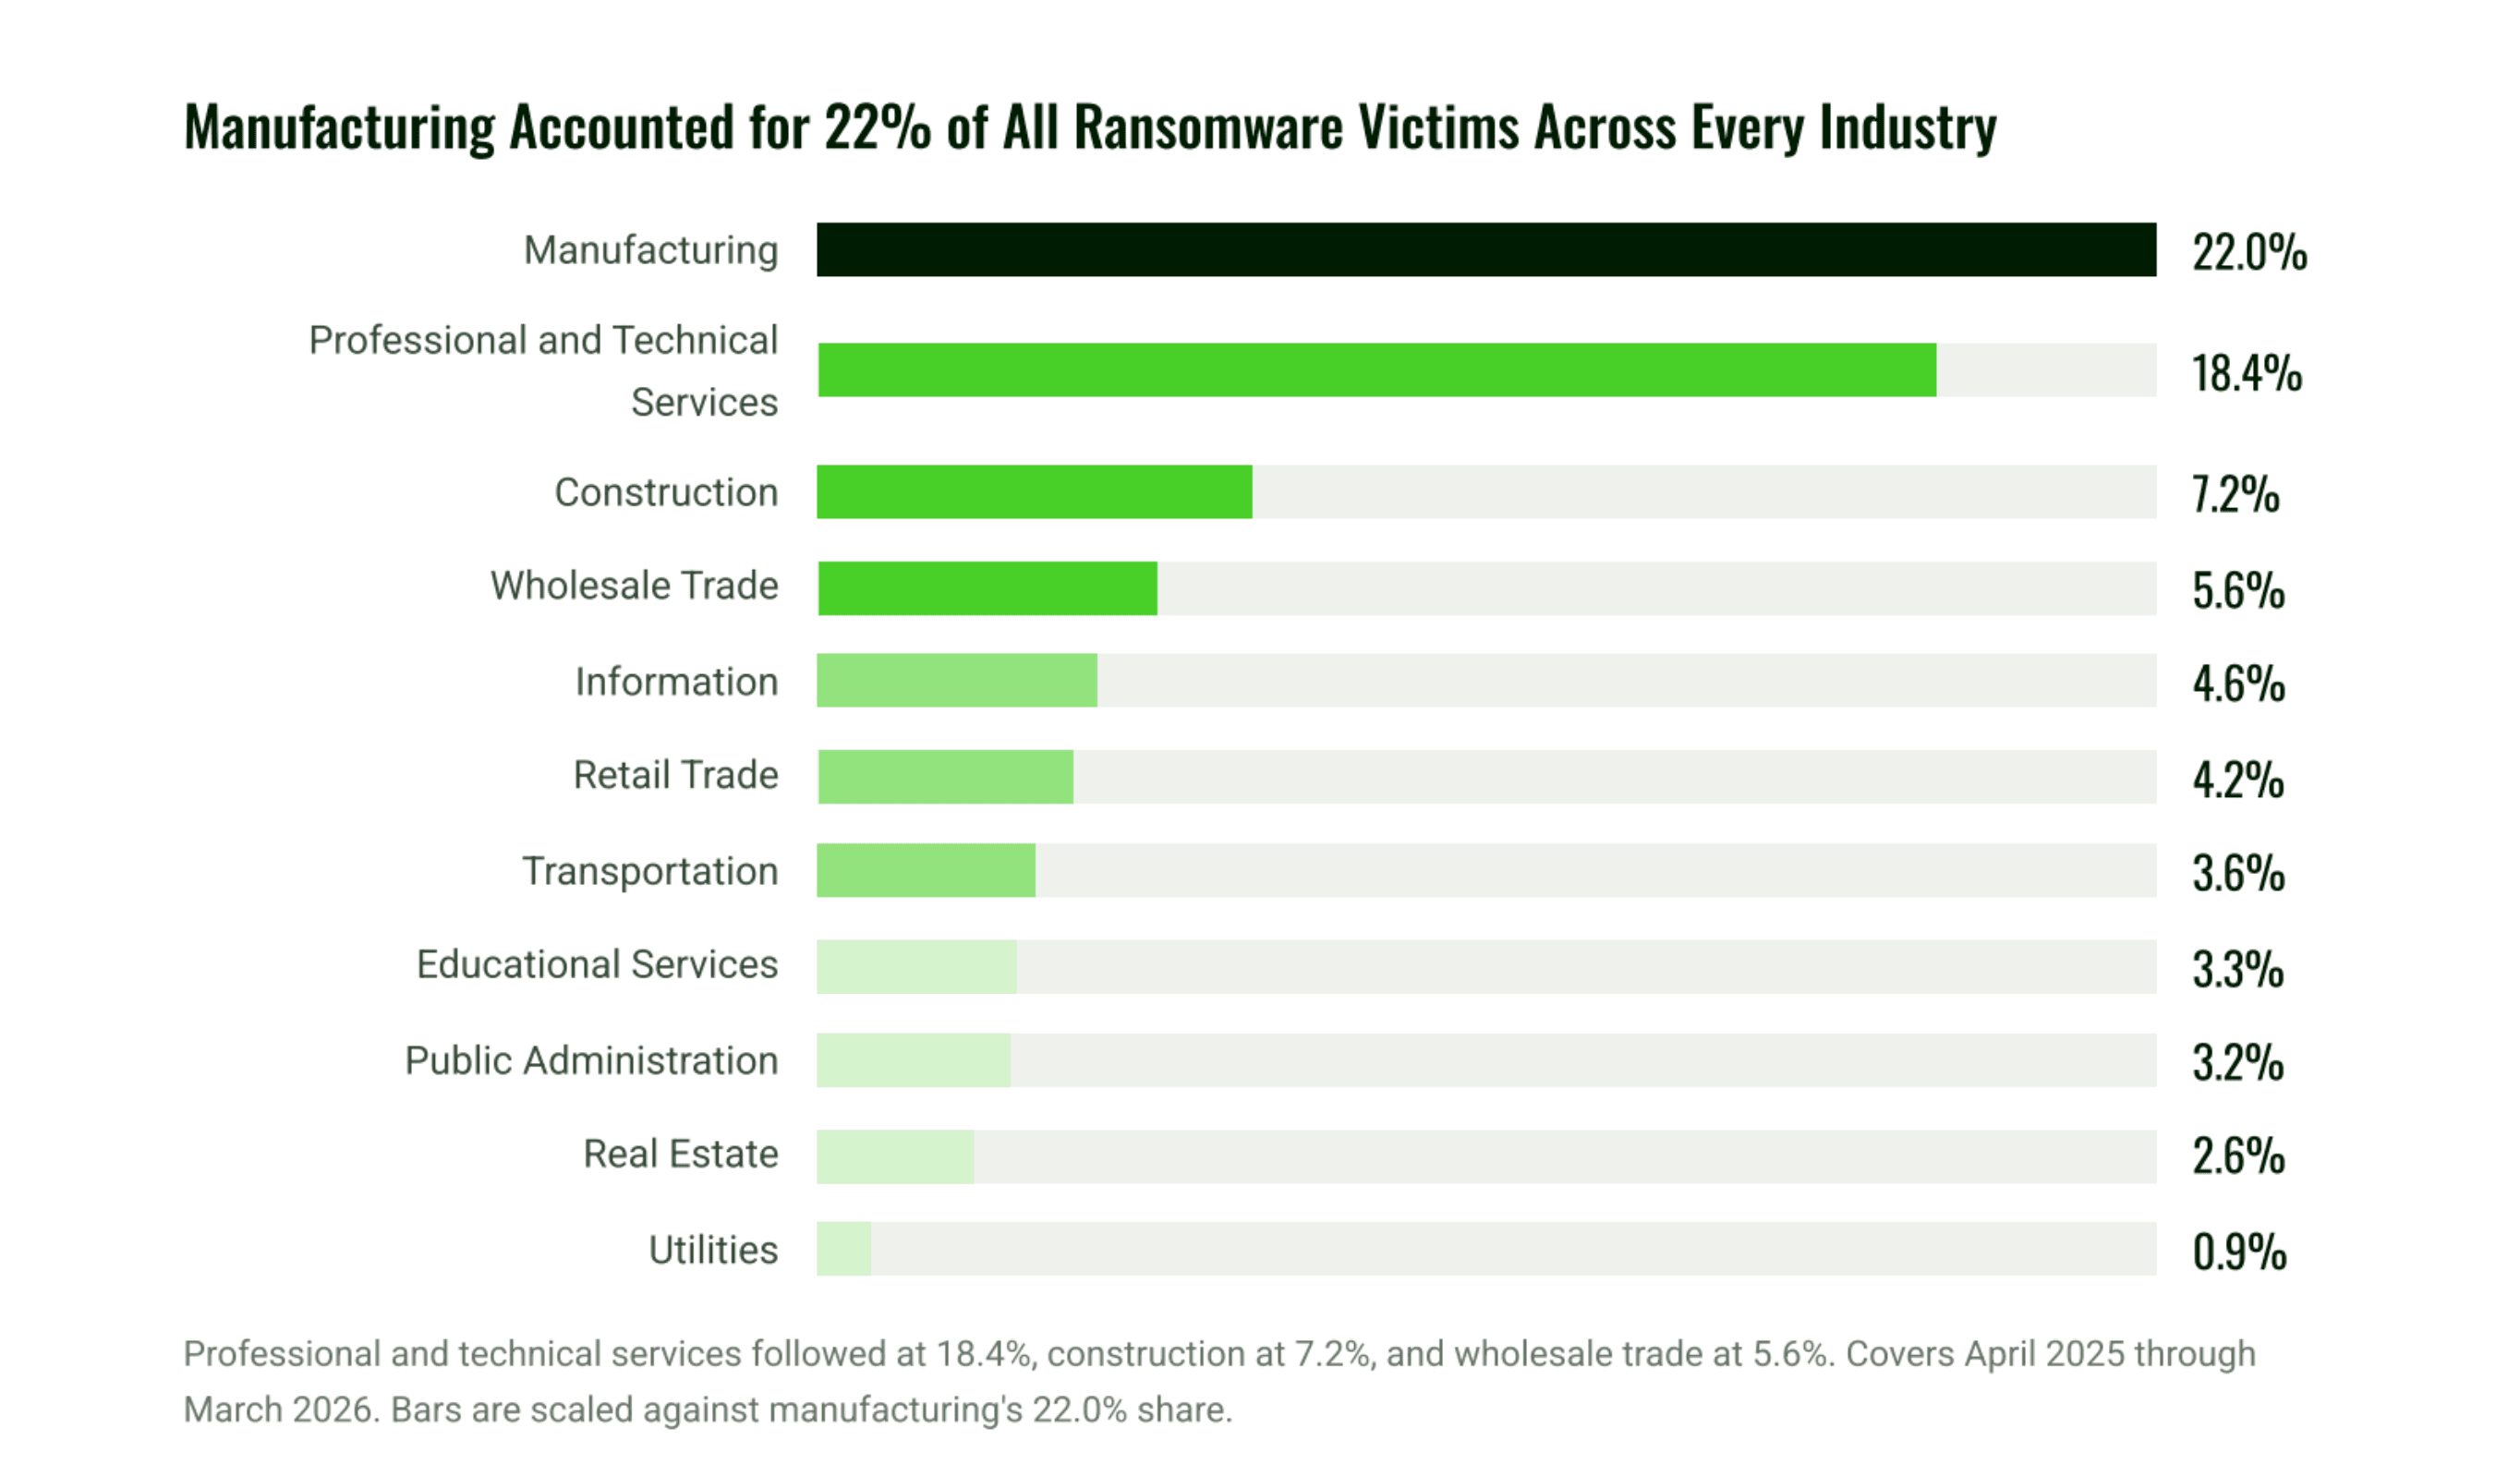
Manufacturing has held the number one spot for ransomware attacks for five consecutive years: 22.0% of every disclosed victim across every industry Black Kite tracks. But the exposure doesn't stop at your own network. It arrives through suppliers you don't fully see, and when a manufacturer appears on a leak site, it cascades into the vendor list of everyone downstream.
Ferhat Dikbiyik, Chief Research & Intelligence Officer, Black Kite"Manufacturing industry's greatest vulnerability isn't its own network. It's the massive, interconnected supply chain that keeps the business running."
See the full findings in the 2026 Manufacturing & Distribution Ransomware Report.
Unmask Your Supply Chain's Silent Threats
The threat isn't rare or isolated. It's structural, and the data shows exactly where it lives.
Manufacturing cyber risk, by the numbers:
Metric | Finding |
Year-over-year growth | Manufacturing ransomware victims up 39.7% in the first seven months of 2026 |
Critical vulnerabilities | 74.8% of the Top 1000 manufacturers carry at least one |
CISA KEV-listed exposure | 54.2% of the Top 1000 (down from 67% in 2024) |
Credentials in stealer log markets | 69.1% of the Top 1000 |
Mid-market concentration | 70.2% of victims generate $10M-$100M in annual revenue |
RSI at disclosure | 74.4% of victims were already in the critical range |
Source: Black Kite 2026 Manufacturing & Distribution Ransomware Report
The pattern holds up close, too. Before their 2025 breaches became public, Asahi Group Holdings and Coca-Cola's Fairlife dairy unit both scored in the upper Ransomware Susceptibility Index® (RSI™) bands, 0.778 and 0.58, ranges where Black Kite's research shows a company is dozens of times more likely to be hit. Asahi's attack still took 30 factories offline and closed six breweries for a week.
Get the complete picture in the 2026 Manufacturing & Distribution Ransomware Report.
We Give You the Intelligence to Fight Back
Here's how Black Kite can help you monitor and defend against supply chain cyber risks.
Anticipate Ransomware Attacks to Protect Your Supply Chain
Manufacturing has held the top ransomware target for five years running. RSI is Black Kite's answer. It's a proprietary score built to predict which suppliers are likely to be hit next, calibrated against thousands of confirmed ransomware victims. Three out of four manufacturing ransomware victims were already in the critical RSI range before their breach became public.
Here's what powers that score:
- Draws on externally observable signals, exposed remote access, exploitable vulnerabilities, leaked credentials, and stealer log activity, the same conditions ransomware operators scan for themselves
- Scores every supplier non-intrusively, for example an RSI of 0.456 against a 0.4 critical threshold, with no questionnaire or cooperation required
- Refreshes automatically as a supplier's exposure changes, keeping the score current between review cycles
- Prioritizes remediation by evidence, showing you which suppliers need attention first
Learn more about Ransomware Susceptibility Index® (RSI™).

Proactively Shield Against Supply Chain Disruptions
Minor incidents at a single supplier rarely stay minor. When Jaguar Land Rover's systems went down in 2025, production stopped for five weeks and the disruption reached more than 5,000 organizations across its supplier network, most of them small and mid-sized companies most third-party programs never see.
Black Kite's approach to supply chain cyber risk management extends past your direct suppliers. Through supply chain risk monitoring, the platform maps fourth- and fifth-party dependencies automatically, surfacing the weak link before it becomes a production problem.
Here's what that gives your team.
- Map Nth-party suppliers and inventory automatically, exposing corners of your ecosystem you didn't know existed
- Identify exposed fourth parties when a new vulnerability or campaign emerges, before anyone in your chain is compromised
- Flag geopolitical strife and natural disasters affecting your supply chain before they turn into a production delay
- Account for competitive advantage loss, including intellectual property and trade secrets, as a modeled loss category
Learn more about Nth-Party Visibility and Geopolitical Monitoring.

Align Supplier Risk With Manufacturing Compliance Requirements
Manufacturers answer to more binding requirements than most industries now. NIS2 names manufacturing in scope by name, with fines up to €10 million and personal liability reaching management.
The UK's Cyber Security and Resilience Bill and the US CMMC program are pushing supplier security from best practice toward a condition of doing business. ISA/IEC 62443 and NIST Manufacturing Profiles set the technical bar underneath all of it.
Here's how Black Kite keeps you ahead of it.
- Cross-correlates supplier cyber risk findings to NIS2 Article 21 and CMMC 2.0 requirements automatically, with ISA/IEC 62443 available as an admin-built custom framework on Premium and Assess
- Gives your team one compliance view across the supply chain, covering every framework and every supplier
- Produces documentation ready to hand to auditors, customers, regulators, or your board
In Black Kite's platform, that shows up as a single compliance rating, for example 70% against a target framework, broken down by the specific controls driving the gap.
Learn more about AI-powered Cyber Assessments and Custom Cyber Assessment Frameworks.

Quantify Risk for Operational Continuity
A dollar figure moves faster than a risk score, especially in manufacturing, where the CIO function often reports through the CFO.
Jaguar Land Rover's five-week shutdown cost an estimated £1.9 billion across more than 5,000 supplier organizations. Open FAIR™-based quantification gets you a comparable number before a disruption reaches that scale.
Here's what that looks like in practice:
- Forecasts the financial exposure of a supplier cyber incident or supply chain disruption, using Open FAIR™
- Separates exposure by scenario, a data breach, ransomware, or business interruption, so budgets start with a real number
- Translates technical findings into terms your leadership already speaks
In Black Kite's platform, that shows up as modeled exposure per scenario, for example $743.5K from a ransomware scenario, with separate figures for data breach and business interruption.
Learn more about Cyber Risk Quantification.

What's the Difference Between Supplier Risk and OT/ICS Security?
Manufacturing cyber risk covers two different problems, and each needs its own tool.
Third-Party Supplier Risk (Black Kite) | OT/ICS Floor Security | |
What it covers | Cyber posture of suppliers, vendors, and Nth-party dependencies connected to your operations | Industrial control systems, PLCs, sensors, and plant-floor networks |
How it works | Continuous, outside-in monitoring and standards-based ratings, no supplier cooperation required | Network segmentation, asset discovery, and threat detection running on the OT network itself |
What breaks without it | A supplier breach goes undetected until it disrupts production or exposes data | An attack on plant equipment goes undetected until it causes physical downtime |
Who typically owns it | CISO, supply chain risk manager, procurement, GRC | Plant operations, OT security engineering |
Black Kite covers the first column. Pair it with a dedicated OT/ICS platform for the second, and both sides of manufacturing cyber risk are covered, each handled by the tool built for it.
Manufacturing Cyber Risk FAQs
Protect Your Manufacturing Organization from Third-Party Cyber Risk
Manufacturing has been ransomware's top target for five years running. See what your suppliers are hiding.